Our services
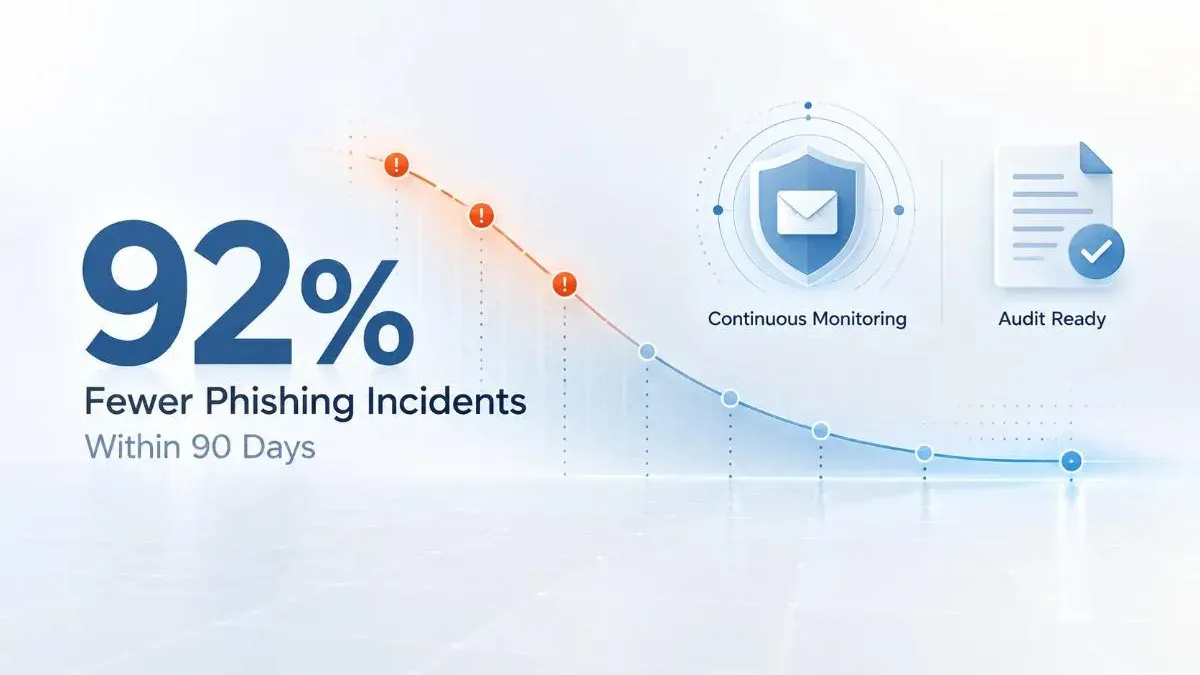
A layered Microsoft 365 security framework, aligned with NIST and CIS, that cut phishing incidents by 92% in 90 days.
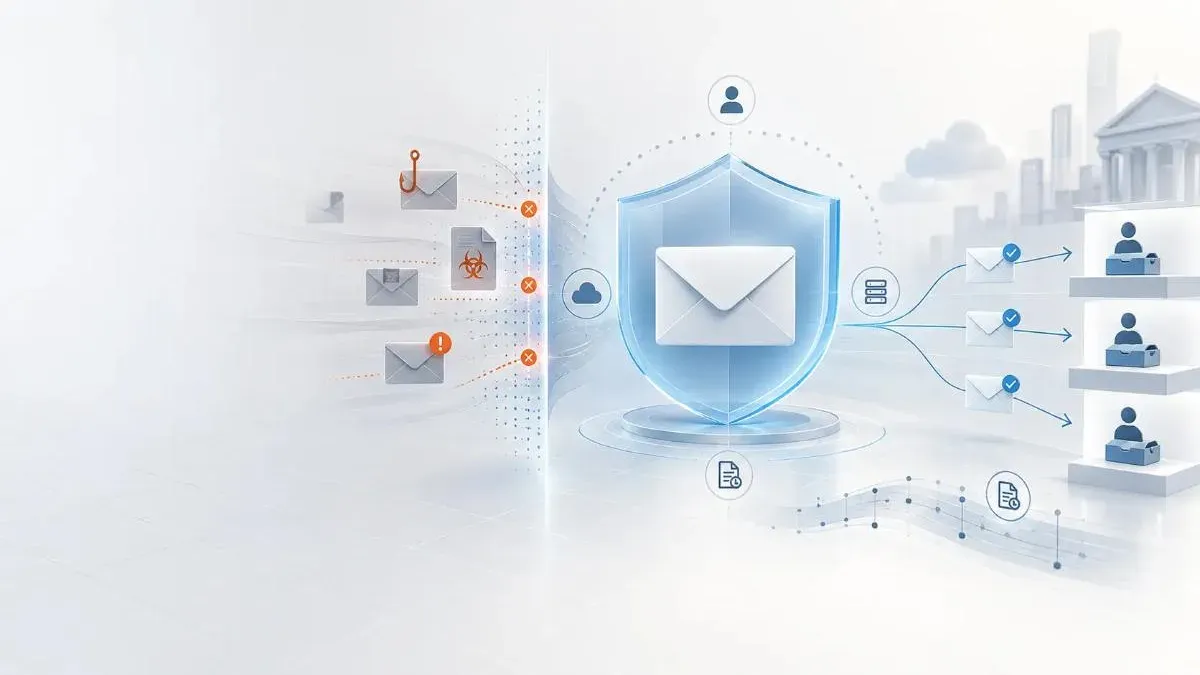
The firm relied on Exchange Online for daily communication and sensitive information. Repeated phishing attempts put accounts and data at risk.
Five layers, aligned with the NIST Cybersecurity Framework and CIS Controls.
Email threat protection
Exchange Online Protection and Microsoft Defender for Office 365 strengthened defenses against phishing, spam and malicious content.
Identity and access
Multi-factor authentication and Conditional Access policies reduced the risk of unauthorized account access.
Email authentication
SPF, DKIM and DMARC verify legitimate senders and prevent domain impersonation.
Mailbox audit logging
Detailed mailbox audit logging improved visibility into access and user activity for investigations and compliance.
Continuous monitoring
Ongoing monitoring aligned with NIST and CIS practices identifies risks as they appear.
Tell us what you run and get a clear quote that lists every user, server and device we would cover.